#include "suricata-common.h"#include "detect.h"#include "detect-engine.h"#include "detect-engine-address.h"#include "detect-engine-port.h"#include "detect-engine-mpm.h"#include "detect-engine-state.h"#include "detect-engine-build.h"#include "detect-content.h"#include "detect-bsize.h"#include "detect-isdataat.h"#include "detect-pcre.h"#include "detect-uricontent.h"#include "detect-reference.h"#include "detect-ipproto.h"#include "detect-flow.h"#include "detect-app-layer-protocol.h"#include "detect-lua.h"#include "detect-app-layer-event.h"#include "detect-http-method.h"#include "pkt-var.h"#include "host.h"#include "util-profiling.h"#include "decode.h"#include "flow.h"#include "util-rule-vars.h"#include "conf.h"#include "conf-yaml-loader.h"#include "app-layer.h"#include "app-layer-protos.h"#include "app-layer-parser.h"#include "app-layer-htp.h"#include "util-classification-config.h"#include "util-unittest-helper.h"#include "util-debug.h"#include "string.h"#include "detect-parse.h"#include "detect-engine-iponly.h"#include "detect-engine-file.h"#include "app-layer-detect-proto.h"#include "action-globals.h"#include "util-validate.h"#include "detect-engine-alert.h"#include "packet.h"#include "tests/detect-parse.c"
Go to the source code of this file.
Data Structures | |
| struct | SigDuplWrapper_ |
| Registration table for file handlers. More... | |
| struct | SignatureParser_ |
| struct | FirewallPolicyChain |
| Ordered, most-specific-first list of config paths a single policy can be configured at. More... | |
| struct | FwPolicyStateRenameHint |
Macros | |
| #define | FW_POLICY_YAML_PATH_MAX 320 |
| max length of a firewall.policies YAML config path More... | |
| #define | FW_POLICY_YAML_PATH_NAME_MAX 64 |
| max length of a single YAML path leaf segment (a hook or sub state name) More... | |
| #define | FW_POLICY_CHAIN_MAX 6 |
| max number of config paths consulted to resolve one policy More... | |
| #define | CASE_CODE_STRING(E, S) case E: return S; break |
| #define | CASE_CODE(E) case E: return #E |
| #define | URL "https://suricata.io/our-story/deprecation-policy/" |
Typedefs | |
| typedef struct SigDuplWrapper_ | SigDuplWrapper |
| Registration table for file handlers. More... | |
| typedef struct SignatureParser_ | SignatureParser |
| typedef struct FirewallPolicyChain | FirewallPolicyChain |
| Ordered, most-specific-first list of config paths a single policy can be configured at. More... | |
Enumerations | |
| enum | DetectFirewallPolicyClass { DETECT_FIREWALL_POLICY_CLASS_PACKET, DETECT_FIREWALL_POLICY_CLASS_PACKET_PRE_FLOW, DETECT_FIREWALL_POLICY_CLASS_APP } |
Functions | |
| const char * | DetectListToHumanString (int list) |
| const char * | DetectListToString (int list) |
| int | DetectEngineContentModifierBufferSetup (DetectEngineCtx *de_ctx, Signature *s, const char *arg, int sm_type, int sm_list, AppProto alproto) |
| SigMatch * | SigMatchAlloc (void) |
| void | SigMatchFree (DetectEngineCtx *de_ctx, SigMatch *sm) |
| free a SigMatch More... | |
| bool | SCSigMatchSilentErrorEnabled (const DetectEngineCtx *de_ctx, uint16_t id) |
| bool | SigMatchStrictEnabled (const enum DetectKeywordId id) |
| void | SigTableApplyStrictCommandLineOption (const char *str) |
| SigMatch * | SCSigMatchAppendSMToList (DetectEngineCtx *de_ctx, Signature *s, uint16_t type, SigMatchCtx *ctx, const int list) |
| Append a SigMatch to the list type. More... | |
| void | SigMatchRemoveSMFromList (Signature *s, SigMatch *sm, int sm_list) |
| SigMatch * | DetectGetLastSMFromMpmLists (const DetectEngineCtx *de_ctx, const Signature *s) |
| get the last SigMatch from lists that support MPM. More... | |
| SigMatch * | SCDetectGetLastSMFromLists (const Signature *s,...) |
| Returns the sm with the largest index (added latest) from the lists passed to us. More... | |
| SigMatch * | DetectGetLastSMByListPtr (const Signature *s, SigMatch *sm_list,...) |
| Returns the sm with the largest index (added last) from the list passed to us as a pointer. More... | |
| SigMatch * | DetectGetLastSMByListId (const Signature *s, int list_id,...) |
| Returns the sm with the largest index (added last) from the list passed to us as an id. More... | |
| const SigMatch * | SCDetectSignatureGetLastSMByType (const Signature *s, int list_id, uint16_t type) |
| Get the last SigMatch of keyword type in list list_id. More... | |
| const SigMatch * | SCSigMatchGetPrevByType (const SigMatch *sm, uint16_t type) |
| Get the previous SigMatch of keyword type before sm. More... | |
| const SigMatchCtx * | SCSigMatchGetCtx (const SigMatch *sm) |
| Get the keyword context of sm, as passed to SCSigMatchAppendSMToList() by the keyword's Setup callback. More... | |
| SigMatch * | DetectGetLastSM (const Signature *s) |
| Returns the sm with the largest index (added latest) from this sig. More... | |
| int | SigMatchListSMBelongsTo (const Signature *s, const SigMatch *key_sm) |
| const char * | DetectFirewallAppGenericHookName (const uint8_t state, const uint8_t complete_state, const int direction) |
| Generic start/complete hook alias for an app progress state, in config form (hyphens), or NULL for intermediate states. More... | |
| void | DetectRegisterAppLayerHookLists (void) |
| register app hooks as generic lists More... | |
| void | DetectListSupportedProtocols (void) |
| int | SignatureInitDataBufferCheckExpand (Signature *s) |
| check if buffers array still has space left, expand if not More... | |
| Signature * | SigAlloc (void) |
| void | SigFree (DetectEngineCtx *de_ctx, Signature *s) |
| int | DetectSignatureSetMultiAppProto (Signature *s, const AppProto *alprotos) |
| this function is used to set multiple possible app-layer protos More... | |
| bool | SCDetectSetupSignatureIsNegated (const Signature *s) |
| Check if the keyword option being set up was negated. More... | |
| int | SCDetectSignatureSetAppProto (Signature *s, AppProto alproto) |
| SigMatchData * | SigMatchList2DataArray (SigMatch *head) |
| convert SigMatch list to SigMatchData array More... | |
| Signature * | SigInit (DetectEngineCtx *de_ctx, const char *sigstr) |
| Parses a signature and adds it to the Detection Engine Context. More... | |
| int | DetectParseDupSigHashInit (DetectEngineCtx *de_ctx) |
| Initializes the hash table that is used to cull duplicate sigs. More... | |
| void | DetectParseDupSigHashFree (DetectEngineCtx *de_ctx) |
| Frees the hash table that is used to cull duplicate sigs. More... | |
| Signature * | DetectFirewallRuleAppendNew (DetectEngineCtx *de_ctx, const char *sigstr) |
| Parse and append a Signature into the Detection Engine Context signature list. More... | |
| Signature * | DetectEngineAppendSig (DetectEngineCtx *de_ctx, const char *sigstr) |
| Parse and append a Signature into the Detection Engine Context signature list. More... | |
| int | DetectParsePcreExec (DetectParseRegex *parse_regex, pcre2_match_data **match, const char *str, int start_offset, int options) |
| void | DetectParseFreeRegex (DetectParseRegex *r) |
| void | DetectParseFreeRegexes (void) |
| void | DetectParseRegexAddToFreeList (DetectParseRegex *detect_parse) |
| add regex and/or study to at exit free list More... | |
| bool | DetectSetupParseRegexesOpts (const char *parse_str, DetectParseRegex *detect_parse, int opts) |
| DetectParseRegex * | DetectSetupPCRE2 (const char *parse_str, int opts) |
| int | SC_Pcre2SubstringCopy (pcre2_match_data *match_data, uint32_t number, PCRE2_UCHAR *buffer, PCRE2_SIZE *bufflen) |
| int | SC_Pcre2SubstringGet (pcre2_match_data *match_data, uint32_t number, PCRE2_UCHAR **bufferptr, PCRE2_SIZE *bufflen) |
| void | DetectSetupParseRegexes (const char *parse_str, DetectParseRegex *detect_parse) |
| const char * | ActionScopeToString (enum ActionScope s) |
| void | DetectFirewallPolicyToString (const struct DetectFirewallPolicy *p, char *out, size_t out_size) |
| int | DetectFirewallInitDefaultPolicies (DetectEngineCtx *de_ctx) |
| allocate and initialize to default values the policies table More... | |
| int | DetectFirewallLoadDefaultPolicies (DetectEngineCtx *de_ctx) |
| void | DetectParseRegisterTests (void) |
| this function registers unit tests for DetectParse More... | |
| void | SigParseRegisterTests (void) |
Variables | |
| SigTableElmt * | sigmatch_table = NULL |
| bool | sc_set_caps |
| int | g_skip_prefilter |
Detailed Description
signature parser
Definition in file detect-parse.c.
Macro Definition Documentation
◆ CASE_CODE
| #define CASE_CODE | ( | E | ) | case E: return #E |
Definition at line 167 of file detect-parse.c.
◆ CASE_CODE_STRING
| #define CASE_CODE_STRING | ( | E, | |
| S | |||
| ) | case E: return S; break |
◆ FW_POLICY_CHAIN_MAX
| #define FW_POLICY_CHAIN_MAX 6 |
max number of config paths consulted to resolve one policy
Definition at line 139 of file detect-parse.c.
◆ FW_POLICY_YAML_PATH_MAX
| #define FW_POLICY_YAML_PATH_MAX 320 |
max length of a firewall.policies YAML config path
Definition at line 135 of file detect-parse.c.
◆ FW_POLICY_YAML_PATH_NAME_MAX
| #define FW_POLICY_YAML_PATH_NAME_MAX 64 |
max length of a single YAML path leaf segment (a hook or sub state name)
Definition at line 137 of file detect-parse.c.
◆ URL
| #define URL "https://suricata.io/our-story/deprecation-policy/" |
Typedef Documentation
◆ FirewallPolicyChain
| typedef struct FirewallPolicyChain FirewallPolicyChain |
Ordered, most-specific-first list of config paths a single policy can be configured at.
◆ SigDuplWrapper
| typedef struct SigDuplWrapper_ SigDuplWrapper |
Registration table for file handlers.
We use this as data to the hash table DetectEngineCtx->dup_sig_hash_table.
◆ SignatureParser
| typedef struct SignatureParser_ SignatureParser |
helper structure for sig parsing
Enumeration Type Documentation
◆ DetectFirewallPolicyClass
Valid action scopes per firewall hook class.
| Enumerator | |
|---|---|
| DETECT_FIREWALL_POLICY_CLASS_PACKET | |
| DETECT_FIREWALL_POLICY_CLASS_PACKET_PRE_FLOW | |
| DETECT_FIREWALL_POLICY_CLASS_APP | |
Definition at line 112 of file detect-parse.c.
Function Documentation
◆ ActionScopeToString()
| const char* ActionScopeToString | ( | enum ActionScope | s | ) |
Definition at line 4265 of file detect-parse.c.
References ACTION_SCOPE_AUTO, ACTION_SCOPE_FLOW, ACTION_SCOPE_HOOK, ACTION_SCOPE_PACKET, ACTION_SCOPE_TX, and DEBUG_VALIDATE_BUG_ON.
Referenced by DetectFirewallPolicyToString().

◆ DetectEngineAppendSig()
| Signature* DetectEngineAppendSig | ( | DetectEngineCtx * | de_ctx, |
| const char * | sigstr | ||
| ) |
Parse and append a Signature into the Detection Engine Context signature list.
If the signature is bidirectional it should append two signatures (with the addresses switched) into the list. Also handle duplicate signatures. In case of duplicate sigs, use the ones that have the latest revision. We use the sid and the msg to identify duplicate sigs. If 2 sigs have the same sid and gid, they are duplicates.
- Parameters
-
de_ctx Pointer to the Detection Engine Context. sigstr Pointer to a character string containing the signature to be parsed. sig_file Pointer to a character string containing the filename from which signature is read lineno Line number from where signature is read
- Return values
-
Pointer to the head Signature in the detection engine ctx sig_list on success; NULL on failure.
In DetectEngineAppendSig(), the signatures are prepended and we always return the first one so if the signature is bidirectional, the returned sig will point through "next" ptr to the cloned signatures with the switched addresses
Definition at line 4045 of file detect-parse.c.
References de_ctx, and SigInit().
Referenced by UTHAppendSigs(), UTHPacketMatchSig(), UTHPacketMatchSigMpm(), and UTHParseSignature().


◆ DetectEngineContentModifierBufferSetup()
| int DetectEngineContentModifierBufferSetup | ( | DetectEngineCtx * | de_ctx, |
| Signature * | s, | ||
| const char * | arg, | ||
| int | sm_type, | ||
| int | sm_list, | ||
| AppProto | alproto | ||
| ) |
- Parameters
-
arg NULL or empty string
Definition at line 183 of file detect-parse.c.
References Signature_::alproto, ALPROTO_UNKNOWN, DETECT_SM_LIST_NOTSET, Signature_::init_data, SignatureInitData_::list, name, SCLogError, and sigmatch_table.
Referenced by DetectHttpUriSetup().

◆ DetectFirewallAppGenericHookName()
| const char* DetectFirewallAppGenericHookName | ( | const uint8_t | state, |
| const uint8_t | complete_state, | ||
| const int | direction | ||
| ) |
Generic start/complete hook alias for an app progress state, in config form (hyphens), or NULL for intermediate states.
Definition at line 1253 of file detect-parse.c.
◆ DetectFirewallInitDefaultPolicies()
| int DetectFirewallInitDefaultPolicies | ( | DetectEngineCtx * | de_ctx | ) |
allocate and initialize to default values the policies table
Definition at line 4574 of file detect-parse.c.
References DetectFirewallPolicies::app_policies, HashTableInit(), and SCCalloc.

◆ DetectFirewallLoadDefaultPolicies()
| int DetectFirewallLoadDefaultPolicies | ( | DetectEngineCtx * | de_ctx | ) |
Definition at line 4921 of file detect-parse.c.
References DetectEngineCtx_::config_prefix, de_ctx, and DetectEngineCtx_::fw_policies.
◆ DetectFirewallPolicyToString()
| void DetectFirewallPolicyToString | ( | const struct DetectFirewallPolicy * | p, |
| char * | out, | ||
| size_t | out_size | ||
| ) |
Definition at line 4283 of file detect-parse.c.
References Packet_::action, ACTION_ACCEPT, ACTION_ALERT, ACTION_DROP, ACTION_PASS, ACTION_REJECT_ANY, ACTION_REJECT_BOTH, ACTION_REJECT_DST, ACTION_SCOPE_FLOW, ActionScopeToString(), DEBUG_VALIDATE_BUG_ON, p, and strlcat().

◆ DetectFirewallRuleAppendNew()
| Signature* DetectFirewallRuleAppendNew | ( | DetectEngineCtx * | de_ctx, |
| const char * | sigstr | ||
| ) |
Parse and append a Signature into the Detection Engine Context signature list.
If the signature is bidirectional it should append two signatures (with the addresses switched) into the list. Also handle duplicate signatures. In case of duplicate sigs, use the ones that have the latest revision. We use the sid and the msg to identify duplicate sigs. If 2 sigs have the same sid and gid, they are duplicates.
- Parameters
-
de_ctx Pointer to the Detection Engine Context. sigstr Pointer to a character string containing the signature to be parsed. sig_file Pointer to a character string containing the filename from which signature is read lineno Line number from where signature is read
- Return values
-
Pointer to the head Signature in the detection engine ctx sig_list on success; NULL on failure.
In DetectEngineAppendSig(), the signatures are prepended and we always return the first one so if the signature is bidirectional, the returned sig will point through "next" ptr to the cloned signatures with the switched addresses
Definition at line 3973 of file detect-parse.c.
◆ DetectGetLastSM()
Returns the sm with the largest index (added latest) from this sig.
- Return values
-
sm_last Pointer to last sm
Definition at line 796 of file detect-parse.c.
References SignatureInitData_::buffer_index, SignatureInitData_::buffers, DETECT_SM_LIST_MAX, SigMatch_::idx, Signature_::init_data, SignatureInitData_::smlists_tail, and SignatureInitDataBuffer_::tail.
◆ DetectGetLastSMByListId()
Returns the sm with the largest index (added last) from the list passed to us as an id.
- Parameters
-
list_id id of the list to be searched va_args list of keyword types terminated by -1
- Return values
-
sm_last to last sm.
Definition at line 694 of file detect-parse.c.
References SignatureInitData_::buffer_index, SignatureInitData_::buffers, DETECT_SM_LIST_MAX, Signature_::init_data, and SignatureInitDataBuffer_::tail.
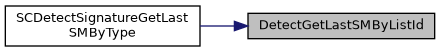
Referenced by SCDetectSignatureGetLastSMByType().
◆ DetectGetLastSMByListPtr()
Returns the sm with the largest index (added last) from the list passed to us as a pointer.
- Parameters
-
sm_list pointer to the SigMatch we should look before va_args list of keyword types terminated by -1
- Return values
-
sm_last to last sm.
Definition at line 662 of file detect-parse.c.
Referenced by DetectGetLastSMFromMpmLists().

◆ DetectGetLastSMFromMpmLists()
| SigMatch* DetectGetLastSMFromMpmLists | ( | const DetectEngineCtx * | de_ctx, |
| const Signature * | s | ||
| ) |
get the last SigMatch from lists that support MPM.
- Note
- only supports the lists that are registered through DetectBufferTypeSupportsMpm().
Definition at line 563 of file detect-parse.c.
References SignatureInitData_::buffer_index, SignatureInitData_::buffers, de_ctx, DETECT_CONTENT, DETECT_SM_LIST_MAX, DetectEngineBufferTypeSupportsMpmGetById(), DetectGetLastSMByListPtr(), SignatureInitDataBuffer_::id, SigMatch_::idx, Signature_::init_data, SignatureInitData_::smlists_tail, and SignatureInitDataBuffer_::tail.

◆ DetectListSupportedProtocols()
| void DetectListSupportedProtocols | ( | void | ) |
Definition at line 1663 of file detect-parse.c.
References AppProtoDetectListNames(), and DetectEngineProtoList().
Referenced by ListRuleProtocols().


◆ DetectListToHumanString()
| const char* DetectListToHumanString | ( | int | list | ) |
Definition at line 149 of file detect-parse.c.
Referenced by DumpPatterns().

◆ DetectListToString()
| const char* DetectListToString | ( | int | list | ) |
Definition at line 167 of file detect-parse.c.
◆ DetectParseDupSigHashFree()
| void DetectParseDupSigHashFree | ( | DetectEngineCtx * | de_ctx | ) |
Frees the hash table that is used to cull duplicate sigs.
- Parameters
-
de_ctx Pointer to the detection engine context that holds this table.
Definition at line 3790 of file detect-parse.c.
References de_ctx, DetectEngineCtx_::dup_sig_hash_table, and HashListTableFree().
Referenced by DetectEngineCtxFree().


◆ DetectParseDupSigHashInit()
| int DetectParseDupSigHashInit | ( | DetectEngineCtx * | de_ctx | ) |
Initializes the hash table that is used to cull duplicate sigs.
- Parameters
-
de_ctx Pointer to the detection engine context.
- Return values
-
0 On success. -1 On failure.
Definition at line 3773 of file detect-parse.c.
References de_ctx, DetectEngineCtx_::dup_sig_hash_table, and HashListTableInit().

◆ DetectParseFreeRegex()
| void DetectParseFreeRegex | ( | DetectParseRegex * | r | ) |
Definition at line 4109 of file detect-parse.c.
References DetectParseRegex::context, and DetectParseRegex::regex.
◆ DetectParseFreeRegexes()
| void DetectParseFreeRegexes | ( | void | ) |
Definition at line 4119 of file detect-parse.c.
Referenced by GlobalsDestroy().

◆ DetectParsePcreExec()
| int DetectParsePcreExec | ( | DetectParseRegex * | parse_regex, |
| pcre2_match_data ** | match, | ||
| const char * | str, | ||
| int | start_offset, | ||
| int | options | ||
| ) |
Definition at line 4099 of file detect-parse.c.
◆ DetectParseRegexAddToFreeList()
| void DetectParseRegexAddToFreeList | ( | DetectParseRegex * | detect_parse | ) |
add regex and/or study to at exit free list
Definition at line 4135 of file detect-parse.c.
References FatalError, DetectParseRegex::next, DetectParseRegex::regex, and SCCalloc.
Referenced by DetectSetupParseRegexesOpts().

◆ DetectParseRegisterTests()
| void DetectParseRegisterTests | ( | void | ) |
this function registers unit tests for DetectParse
Definition at line 146 of file detect-parse.c.
References UtRegisterTest().
Referenced by SigParseRegisterTests().


◆ DetectRegisterAppLayerHookLists()
| void DetectRegisterAppLayerHookLists | ( | void | ) |
register app hooks as generic lists
Register each hook in each app protocol as: <alproto>:<hook name>:generic These lists can be used by lua scripts to hook into.
- Todo:
- move elsewhere? maybe a detect-engine-hook.c?
Definition at line 1271 of file detect-parse.c.
References ALPROTO_FAILED, AppLayerParserGetMaxSubState(), AppLayerParserGetSubStateCompletion(), AppLayerParserGetSubStateName(), AppLayerParserGetSubStateProgressName(), AppLayerParserSupportsSubStates(), AppProtoToStringRaw(), BUG_ON, DetectAppLayerInspectEngineRegisterSubState(), DetectEngineInspectGenericList(), g_alproto_max, SCLogDebug, SIG_FLAG_TOCLIENT, and SIG_FLAG_TOSERVER.
Referenced by SigTableSetup().


◆ DetectSetupParseRegexes()
| void DetectSetupParseRegexes | ( | const char * | parse_str, |
| DetectParseRegex * | detect_parse | ||
| ) |
Definition at line 4225 of file detect-parse.c.
References DetectSetupParseRegexesOpts(), and FatalError.

◆ DetectSetupParseRegexesOpts()
| bool DetectSetupParseRegexesOpts | ( | const char * | parse_str, |
| DetectParseRegex * | detect_parse, | ||
| int | opts | ||
| ) |
Definition at line 4146 of file detect-parse.c.
References DetectParseRegex::context, DetectParseRegexAddToFreeList(), DetectParseRegex::regex, SC_MATCH_LIMIT_DEFAULT, SC_MATCH_LIMIT_RECURSION_DEFAULT, and SCLogError.
Referenced by DetectSetupParseRegexes().


◆ DetectSetupPCRE2()
| DetectParseRegex* DetectSetupPCRE2 | ( | const char * | parse_str, |
| int | opts | ||
| ) |
Definition at line 4175 of file detect-parse.c.
References DetectParseRegex::next, DetectParseRegex::regex, SCCalloc, SCFree, and SCLogError.
◆ DetectSignatureSetMultiAppProto()
this function is used to set multiple possible app-layer protos
into the current signature (for example ja4 for both tls and quic)
- Parameters
-
s pointer to the Current Signature alprotos an array terminated by ALPROTO_UNKNOWN
- Return values
-
0 on Success -1 on Failure
Definition at line 2592 of file detect-parse.c.
References Signature_::alproto, ALPROTO_UNKNOWN, SignatureInitData_::alprotos, Signature_::init_data, SCDetectSignatureSetAppProto(), and SIG_ALPROTO_MAX.

◆ SC_Pcre2SubstringCopy()
| int SC_Pcre2SubstringCopy | ( | pcre2_match_data * | match_data, |
| uint32_t | number, | ||
| PCRE2_UCHAR * | buffer, | ||
| PCRE2_SIZE * | bufflen | ||
| ) |
Definition at line 4201 of file detect-parse.c.
◆ SC_Pcre2SubstringGet()
| int SC_Pcre2SubstringGet | ( | pcre2_match_data * | match_data, |
| uint32_t | number, | ||
| PCRE2_UCHAR ** | bufferptr, | ||
| PCRE2_SIZE * | bufflen | ||
| ) |
Definition at line 4213 of file detect-parse.c.
◆ SCDetectGetLastSMFromLists()
Returns the sm with the largest index (added latest) from the lists passed to us.
- Return values
-
Pointer to Last sm.
Definition at line 600 of file detect-parse.c.
References SignatureInitData_::buffer_index, SignatureInitData_::buffers, DETECT_SM_LIST_NOTSET, SignatureInitDataBuffer_::id, Signature_::init_data, SignatureInitData_::list, and SCLogDebug.
◆ SCDetectSetupSignatureIsNegated()
| bool SCDetectSetupSignatureIsNegated | ( | const Signature * | s | ) |
Check if the keyword option being set up was negated.
Only set for keywords registered with the SIGMATCH_HANDLE_NEGATION flag, in which case the leading '!' is stripped from the option value before it is passed to the keyword's Setup callback.
Note: Must only be called from the Setup callback of the keyword currently being setup.
- Parameters
-
s signature being set up
- Return values
-
true if the option was prefixed with '!'
Definition at line 2684 of file detect-parse.c.
References DEBUG_VALIDATE_BUG_ON, Signature_::init_data, and SignatureInitData_::negated.
◆ SCDetectSignatureGetLastSMByType()
| const SigMatch* SCDetectSignatureGetLastSMByType | ( | const Signature * | s, |
| int | list_id, | ||
| uint16_t | type | ||
| ) |
Get the last SigMatch of keyword type in list list_id.
Lets a keyword Setup callback inspect earlier instances of a keyword in the signature being set up, together with SCSigMatchGetPrevByType() and SCSigMatchGetCtx(), without depending on the SigMatch layout.
Only the static lists from DetectSigmatchListEnum are supported. A dynamic buffer list can have several instances in a signature, each with its own SigMatch chain, so there is no single list to walk.
- Parameters
-
s signature being set up list_id static list to search, e.g. DETECT_SM_LIST_MATCH type keyword id, as returned by SCDetectHelperKeywordRegister()
- Return values
-
sm last SigMatch of type in the list, or NULL if there is none or list_id is not a static list
Definition at line 758 of file detect-parse.c.
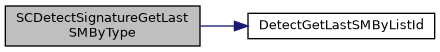
References DEBUG_VALIDATE_BUG_ON, DETECT_SM_LIST_MAX, DetectGetLastSMByListId(), and type.
◆ SCDetectSignatureSetAppProto()
Definition at line 2693 of file detect-parse.c.
Referenced by DetectSignatureSetMultiAppProto().

◆ SCSigMatchAppendSMToList()
| SigMatch* SCSigMatchAppendSMToList | ( | DetectEngineCtx * | de_ctx, |
| Signature * | s, | ||
| uint16_t | type, | ||
| SigMatchCtx * | ctx, | ||
| const int | list | ||
| ) |
Append a SigMatch to the list type.
- Parameters
-
s Signature. new The sig match to append. list The list to append to.
Definition at line 424 of file detect-parse.c.
Referenced by DetectContentSetup(), and DetectFlowvarPostMatchSetup().

◆ SCSigMatchGetCtx()
| const SigMatchCtx* SCSigMatchGetCtx | ( | const SigMatch * | sm | ) |
Get the keyword context of sm, as passed to SCSigMatchAppendSMToList() by the keyword's Setup callback.
- Parameters
-
sm SigMatch, must not be NULL
Definition at line 786 of file detect-parse.c.
References SigMatch_::ctx.
◆ SCSigMatchGetPrevByType()
Get the previous SigMatch of keyword type before sm.
- Parameters
-
sm SigMatch to search before, must not be NULL type keyword id
- Return values
-
sm previous SigMatch of type in the same list, or NULL if there is none
Definition at line 775 of file detect-parse.c.
◆ SCSigMatchSilentErrorEnabled()
| bool SCSigMatchSilentErrorEnabled | ( | const DetectEngineCtx * | de_ctx, |
| uint16_t | id | ||
| ) |
Definition at line 367 of file detect-parse.c.
References de_ctx, and DetectEngineCtx_::sm_types_silent_error.
◆ SigAlloc()
| Signature* SigAlloc | ( | void | ) |
Definition at line 2314 of file detect-parse.c.
References SignatureInitData_::buffers, SignatureInitData_::buffers_size, DETECT_SM_LIST_NOTSET, Signature_::init_data, SignatureInitData_::is_rule_state_dependant, SignatureInitData_::list, SignatureInitData_::mpm_sm_list, Signature_::prio, SignatureInitData_::rule_state_dependant_sids_idx, SCCalloc, SCFree, and unlikely.
◆ SigFree()
| void SigFree | ( | DetectEngineCtx * | de_ctx, |
| Signature * | s | ||
| ) |
Definition at line 2434 of file detect-parse.c.
References SignatureInitData_::buffer_index, SignatureInitData_::buffers, SignatureInitData_::cidr_dst, SignatureInitData_::cidr_src, DetectEngineTransforms::cnt, de_ctx, DETECT_SM_LIST_MAX, SigTableElmt_::Free, SignatureInitDataBuffer_::head, Signature_::init_data, IPOnlyCIDRListFree(), SigMatch_::next, TransformData_::options, SCFree, sigmatch_table, SigMatchFree(), SignatureInitData_::smlists, TransformData_::transform, DetectEngineTransforms::transforms, and SignatureInitData_::transforms.
Referenced by SigCleanSignatures().


◆ SigInit()
| Signature* SigInit | ( | DetectEngineCtx * | de_ctx, |
| const char * | sigstr | ||
| ) |
Parses a signature and adds it to the Detection Engine Context.
- Parameters
-
de_ctx Pointer to the Detection Engine Context. sigstr Pointer to a character string containing the signature to be parsed.
- Return values
-
Pointer to the Signature instance on success; NULL on failure.
Definition at line 3698 of file detect-parse.c.
Referenced by DetectEngineAppendSig().

◆ SigMatchAlloc()
| SigMatch* SigMatchAlloc | ( | void | ) |
Definition at line 311 of file detect-parse.c.
References SigMatch_::next, SigMatch_::prev, SCCalloc, and unlikely.
◆ SigMatchFree()
| void SigMatchFree | ( | DetectEngineCtx * | de_ctx, |
| SigMatch * | sm | ||
| ) |
free a SigMatch
- Parameters
-
sm SigMatch to free.
free the ctx, for that we call the Free func
Definition at line 325 of file detect-parse.c.
References SigMatch_::ctx, de_ctx, SigTableElmt_::Free, SCFree, sigmatch_table, and SigMatch_::type.
Referenced by DetectIPProtoRemoveAllSMs(), and SigFree().

◆ SigMatchList2DataArray()
| SigMatchData* SigMatchList2DataArray | ( | SigMatch * | head | ) |
convert SigMatch list to SigMatchData array
- Note
- ownership of sm->ctx is transferred to smd->ctx
Definition at line 2829 of file detect-parse.c.
References len.
◆ SigMatchListSMBelongsTo()
Definition at line 850 of file detect-parse.c.
References SignatureInitData_::buffer_index, SignatureInitData_::buffers, SignatureInitDataBuffer_::head, SignatureInitDataBuffer_::id, Signature_::init_data, and SigMatch_::next.
◆ SigMatchRemoveSMFromList()
Definition at line 523 of file detect-parse.c.
References Signature_::init_data, SigMatch_::next, SigMatch_::prev, SignatureInitData_::smlists, and SignatureInitData_::smlists_tail.
Referenced by DetectIPProtoRemoveAllSMs().

◆ SigMatchStrictEnabled()
| bool SigMatchStrictEnabled | ( | const enum DetectKeywordId | id | ) |
Definition at line 372 of file detect-parse.c.
References DETECT_TBLSIZE, flags, SIGMATCH_STRICT_PARSING, and sigmatch_table.
◆ SignatureInitDataBufferCheckExpand()
| int SignatureInitDataBufferCheckExpand | ( | Signature * | s | ) |
check if buffers array still has space left, expand if not
Definition at line 2294 of file detect-parse.c.
References SignatureInitData_::buffer_index, SignatureInitData_::buffers, SignatureInitData_::buffers_size, Signature_::init_data, and SCRealloc.
Referenced by DetectBufferGetActiveList().

◆ SigParseRegisterTests()
| void SigParseRegisterTests | ( | void | ) |
Definition at line 6837 of file detect-parse.c.
References DetectParseRegisterTests(), and UtRegisterTest().
Referenced by SigRegisterTests().


◆ SigTableApplyStrictCommandLineOption()
| void SigTableApplyStrictCommandLineOption | ( | const char * | str | ) |
Definition at line 380 of file detect-parse.c.
References DETECT_TBLSIZE, FatalError, SigTableElmt_::flags, SCStrdup, SIGMATCH_STRICT_PARSING, sigmatch_table, and str.
Variable Documentation
◆ g_skip_prefilter
| int g_skip_prefilter |
Definition at line 1159 of file detect-engine-mpm.c.
◆ sc_set_caps
| bool sc_set_caps |
set caps or not
Definition at line 194 of file suricata.c.
◆ sigmatch_table
| SigTableElmt* sigmatch_table = NULL |
Definition at line 78 of file detect-parse.c.
Referenced by DetectAckRegister(), DetectAppLayerEventRegister(), DetectAppLayerProtocolRegister(), DetectAppLayerStateRegister(), DetectAsn1Register(), DetectBase64DataRegister(), DetectBase64DecodeRegister(), DetectBsizeRegister(), DetectBypassRegister(), DetectByteExtractRegister(), DetectBytejumpRegister(), DetectBytemathRegister(), DetectBytetestRegister(), DetectClasstypeRegister(), DetectConfigRegister(), DetectContentRegister(), DetectCsumRegister(), DetectDatarepRegister(), DetectDatasetRegister(), DetectDepthRegister(), DetectDetectionFilterRegister(), DetectDistanceRegister(), DetectDnsResponseRegister(), DetectDsizeRegister(), DetectEngineAppInspectionEngineSignatureFree(), DetectEngineBufferTypeValidateTransform(), DetectEngineContentModifierBufferSetup(), DetectEngineEventRegister(), DetectEngineInspectGenericList(), DetectEntropyRegister(), DetectEtherhdrRegister(), DetectFastPatternRegister(), DetectFiledataRegister(), DetectFilemagicRegister(), DetectFileMd5Register(), DetectFilenameRegister(), DetectFileSha1Register(), DetectFileSha256Register(), DetectFilesizeRegister(), DetectFilestoreRegister(), DetectFlagsRegister(), DetectFlowAgeRegister(), DetectFlowbitsRegister(), DetectFlowBytesRegister(), DetectFlowBytesToClientRegister(), DetectFlowBytesToServerRegister(), DetectFlowElephantRegister(), DetectFlowintRegister(), DetectFlowPktsRegister(), DetectFlowPktsToClientRegister(), DetectFlowPktsToServerRegister(), DetectFlowRegister(), DetectFlowvarRegister(), DetectFragBitsRegister(), DetectFragOffsetRegister(), DetectFrameRegister(), DetectFtpbounceRegister(), DetectFtpCommandDataRegister(), DetectFtpCommandRegister(), DetectFtpCompletionCodeRegister(), DetectFtpdataRegister(), DetectFtpDynamicPortRegister(), DetectFtpModeRegister(), DetectFtpReplyReceivedRegister(), DetectFtpReplyRegister(), DetectGeoipRegister(), DetectGidRegister(), DetectHostbitsRegister(), DetectHttp2Register(), DetectHttpClientBodyRegister(), DetectHttpCookieRegister(), DetectHttpHeaderNamesRegister(), DetectHttpHeaderRegister(), DetectHttpHHRegister(), DetectHttpMethodRegister(), DetectHttpProtocolRegister(), DetectHttpRawHeaderRegister(), DetectHttpRequestHeaderRegister(), DetectHttpRequestLineRegister(), DetectHttpResponseHeaderRegister(), DetectHttpResponseLineRegister(), DetectHttpServerBodyRegister(), DetectHttpStartRegister(), DetectHttpStatCodeRegister(), DetectHttpStatMsgRegister(), DetectHttpUARegister(), DetectHttpUriRegister(), DetectIcmpIdRegister(), DetectIcmpSeqRegister(), DetectIcmpv4HdrRegister(), DetectICMPv6hdrRegister(), DetectICMPv6mtuRegister(), DetectICodeRegister(), DetectIdRegister(), DetectIGMPHdrRegister(), DetectIGMPTypeRegister(), DetectIPAddrBufferRegister(), DetectIpOptsRegister(), DetectIPProtoRegister(), DetectIPRepRegister(), DetectIpv4hdrRegister(), DetectIpv6hdrRegister(), DetectIsdataatRegister(), DetectITypeRegister(), DetectJa4HashRegister(), DetectL3ProtoRegister(), DetectLuaRegister(), DetectMarkRegister(), DetectMetadataRegister(), DetectMsgRegister(), DetectNoalertRegister(), DetectNocaseRegister(), DetectOffsetRegister(), DetectPcreRegister(), DetectPktDataRegister(), DetectPktvarRegister(), DetectPrefilterRegister(), DetectPriorityRegister(), DetectRawbytesRegister(), DetectReferenceRegister(), DetectReplaceRegister(), DetectRequiresRegister(), DetectRevRegister(), DetectRpcRegister(), DetectSameipRegister(), DetectSCTPChunkCntRegister(), DetectSCTPChunkDataRegister(), DetectSCTPChunkTypeRegister(), DetectSCTPHdrRegister(), DetectSCTPVtagRegister(), DetectSeqRegister(), DetectSidRegister(), DetectSipMethodRegister(), DetectSipUriRegister(), DetectSslStateRegister(), DetectSslVersionRegister(), DetectStreamSizeRegister(), DetectTagRegister(), DetectTargetRegister(), DetectTcphdrRegister(), DetectTcpmssRegister(), DetectTcpSessionRegister(), DetectTcpWscaleRegister(), DetectTemplateRegister(), DetectThresholdRegister(), DetectTlsAlpnRegister(), DetectTlsCertChainLenRegister(), DetectTlsCertsRegister(), DetectTlsFingerprintRegister(), DetectTlsIssuerRegister(), DetectTlsJa3HashRegister(), DetectTlsJa3SHashRegister(), DetectTlsJa3SStringRegister(), DetectTlsJa3StringRegister(), DetectTlsRandomBytesRegister(), DetectTlsRandomRegister(), DetectTlsRandomTimeRegister(), DetectTlsRegister(), DetectTlsSerialRegister(), DetectTlsSniRegister(), DetectTlsSubjectAltNameRegister(), DetectTlsSubjectRegister(), DetectTlsValidityRegister(), DetectTlsVersionRegister(), DetectTosRegister(), DetectTransformLuaxformRegister(), DetectTransformPcrexformRegister(), DetectTtlRegister(), DetectUdphdrRegister(), DetectUricontentRegister(), DetectUrilenRegister(), DetectVlanIdRegister(), DetectVlanLayersRegister(), DetectWindowRegister(), DetectWithinRegister(), DetectXbitsRegister(), EngineAnalysisFP(), EngineAnalysisRules2(), PrefilterSetupRuleGroup(), SCDetectHelperKeywordAliasRegister(), SCDetectHelperKeywordJsonInfoRegister(), SCDetectHelperKeywordPacketMatchRegister(), SCDetectHelperKeywordRegister(), SCDetectHelperKeywordSetCleanCString(), SCDetectHelperNewKeywordId(), SCDetectHelperTransformRegister(), SCSigTableHasKeyword(), SigFree(), SigMatchFree(), SigMatchStrictEnabled(), SigTableApplyStrictCommandLineOption(), SigTableCleanup(), SigTableInit(), SigTableList(), and SigTableRegisterTests().